If you stay too long on one form or get away from your computer, and then go back to fill it in - you may get a TokenMismatchException, because the CSRF token won't be the same. It kinda makes sense, but the problem I recently discovered that it does the same for logout (which is also a form). And that's pretty silly, so how to avoid it?
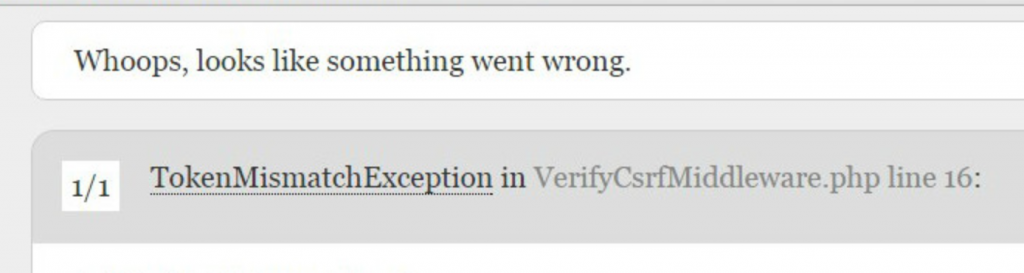
Basically, if you do nothing on the page for a few hours and then click logout, you may see something like this:
 To avoid this, we may add exceptions for the URLs that we don't want to have CSRF protection. There's a special array for that - in app/Http/Middleware/VerifyCsrfToken.php:
class VerifyCsrfToken extends Middleware
{
    /**
     * The URIs that should be excluded from CSRF verification.
     *
     * @var array
     */
    protected $except = [
        //
    ];
}
So what we should do, is add logout into this array:
protected $except = [
    '/logout'
];
You can add more URLs here, if you wish, but be careful - CSRF protection is quite an important thing.

Old post but should we exclude
/logoutfromVerifyCsrfTokenmiddleware in 2026 considering the CSRF risk that could forcibly log out users?